Ubaid Ullah

Ubaid Ullah

Security Engineer

about

I'm a security engineer currently working as a freelancer at HTS Supply and Zyte. At HTS Supply: I run their Cloudflare WAF and test their apps. I also built LLM-based security checks: AI review runs on every pull request, and every new order is screened for fraud the moment it's placed, so risky orders are held and flagged before they ship. While testing, I caught attackers placing free orders through a pricing flaw before a single one shipped.

Most of what I know about defenses comes from years of working around them. I built crawlers that had to get past Cloudflare, Akamai, PerimeterX and Google's bot detection at scale, for data companies like CrawlNow and Zyte. That meant matching TLS fingerprints, patching headless browsers, and reversing obfuscated anti-bot JavaScript. I know how these systems decide who is human and where they fall short, and I use that when I build defenses.

I specialized in Cyber Security during my Computer Science degree, and I still compete. In April 2026 my team took 1st place out of 21 teams in the ToroHack 10.0 CTF.

I also write a lot of code. I won a gold medal at the ICPC Asia West Regional, and I've shipped backends, data pipelines and internal tools in production. I use AI and agentic workflows to automate security and scraping work end to end.

Based in Germany. Remote, open to relocation.

experience

HTS Supply LLC

Aug 2025 to present

Developer and Security Engineer, freelance

  • Found a business logic flaw during testing: "Contact for Price" products carried a hidden price of $0, and attackers were using it to place orders for free. Caught the fraudulent orders before any shipped, closed the flaw, and added detection for zero-value and suspicious orders.
  • Built Cloudflare defenses against competitor price scraping, fake carts and orders, and form spam using custom WAF rules, rate limiting and bot management. Rolled new rules out as challenges first, tuned them against security events, and added skip rules for legitimate services before switching to blocks.
  • Found and locked down publicly exposed files and endpoints.
  • Automated security review with LLMs: an AI reviewer runs on every pull request in CI, and a Shopify order webhook sends each new order for fraud screening. Risky orders are held, tagged and alerted on.
  • Built a custom Shopify app in TypeScript for catalog sync, bulk editing, bulk import and image uploads.
  • Built internal automation for supplier data scraping, price monitoring, catalog cleanup, order reports, and on-demand retrieval of operation manuals from supplier websites.
Zyte

Apr 2025 to present

Python Developer, freelance

  • Build crawlers for large e-commerce targets protected by Cloudflare, Akamai, PerimeterX and Google's bot defenses.
  • Use AI end to end: generating crawlers, detecting blocks and retrying with a new approach, repairing broken selectors, and agentic workflows that run whole fix cycles.
  • AI-driven extraction reached 99% data point coverage on unstructured product pages.
  • Resilient selectors cut data errors by 25% across 10+ projects.

DEMA.shop

Jan 2025 to Mar 2025

Backend Python Developer, freelance

  • Built the MVP backend with FastAPI and event-driven microservices on AWS.
  • Secured the APIs with JWT and OAuth authentication.
  • Set up Dependabot for dependency vulnerabilities and Copilot code analysis on pull requests.
  • Designed RabbitMQ message handling with transactional patterns so no data was lost when services crashed.

CrawlNow

Aug 2022 to Dec 2024

Senior Software Engineer

  • Built 100+ crawlers focused on ban evasion and browser fingerprinting, including authenticated social media targets like Facebook and LinkedIn.
  • Bypassed bot protection with TLS/JA3 fingerprint matching, headless browser patching, reversing anti-bot JavaScript, and residential proxy and session management.
  • Reverse engineered mobile app APIs by hooking apps with Frida and bypassing SSL pinning.
  • Built and owned security for the internal ECS job dashboard (React, Python), which replaced AWS console access for the team:
    • Authentication with role-based permissions, a least-privilege IAM role for the backend, and no AWS secrets in code.
    • Audited it against the OWASP Top 10 and pentested it before rollout.
    • Audit logging of who ran, stopped or changed each job.
    • Automated ongoing checks with Dependabot and static analysis in CI.
  • Built a daily AWS usage monitor with outlier detection and Slack alerts.
  • Cut AWS storage cost by 80% by purging millions of stale files from EFS.

Bayes Esports

2023 to 2025

Live Data Operator, freelance

  • Monitored live match data systems during esports broadcasts and fixed integrity issues in real time.
  • Built a Chrome extension that automated workflows across ProDB, FACEIT and Ubeya, removing a large amount of manual work for operators.

competitions

ToroHack 10.0 CTF

April 2026

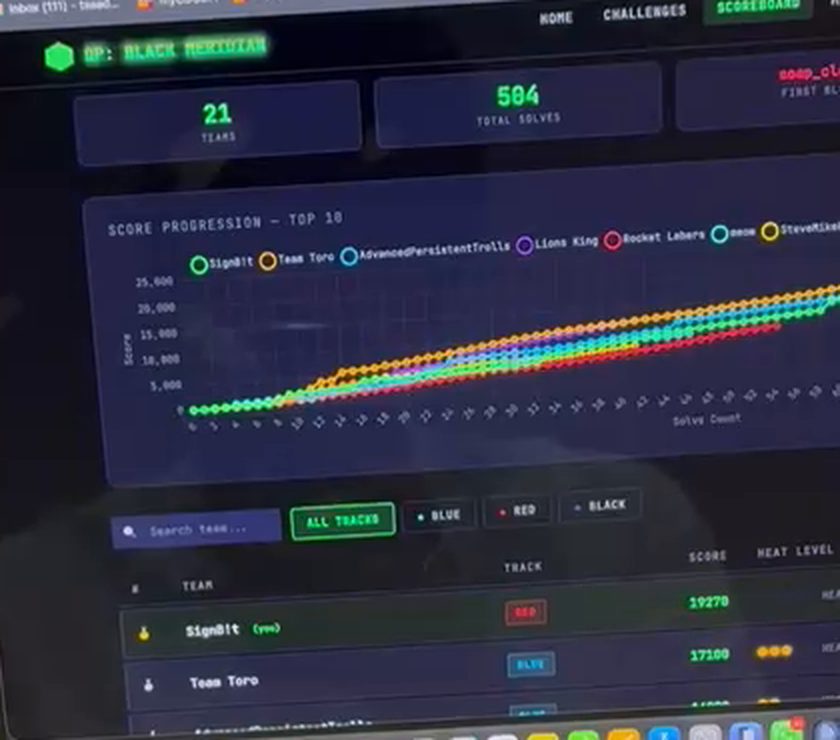
1st place of 21 teams, Red track

The 10th annual Cybersecurity and Hacking Expo at California State University, Dominguez Hills.

  • Won with 19,270 points, about 2,000 ahead of the host school's team in 2nd.
  • Solved challenges across web exploitation, crypto, reversing, forensics, OSINT, pwn and network.
ToroHack 10.0 scoreboard with SignBit in first place at 19,270 points
Scoreboard near the end, filmed on site by a teammate.

ICPC Asia West Topi Regional

2021 contest, held March 2022

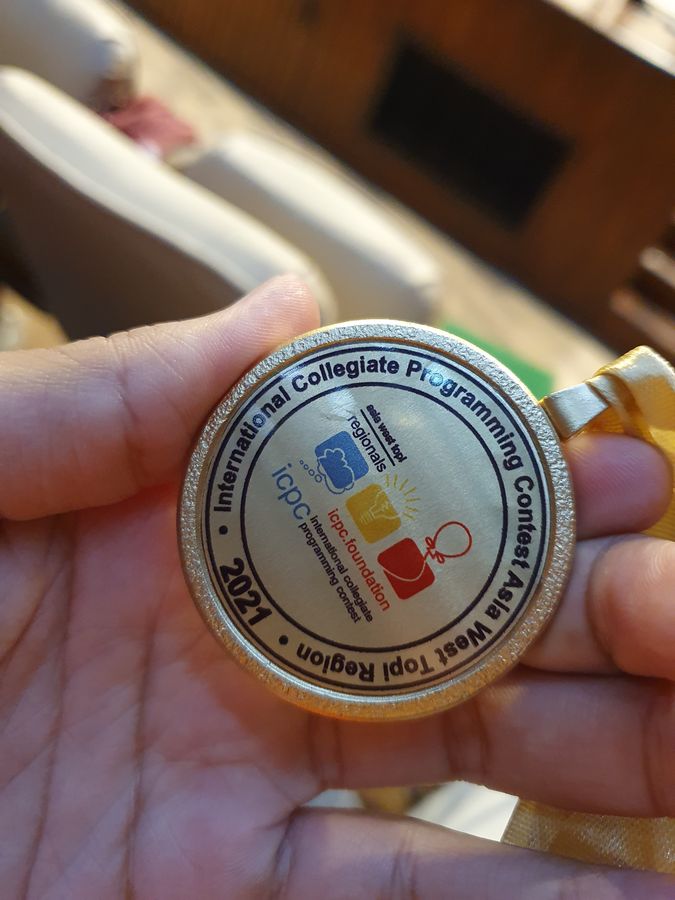
Gold medal, 3rd place of 47 teams

The regional stage of the International Collegiate Programming Contest, the largest university programming competition in the world.

  • 3rd place of 47 teams with team SignBiT from FAST NUCES.
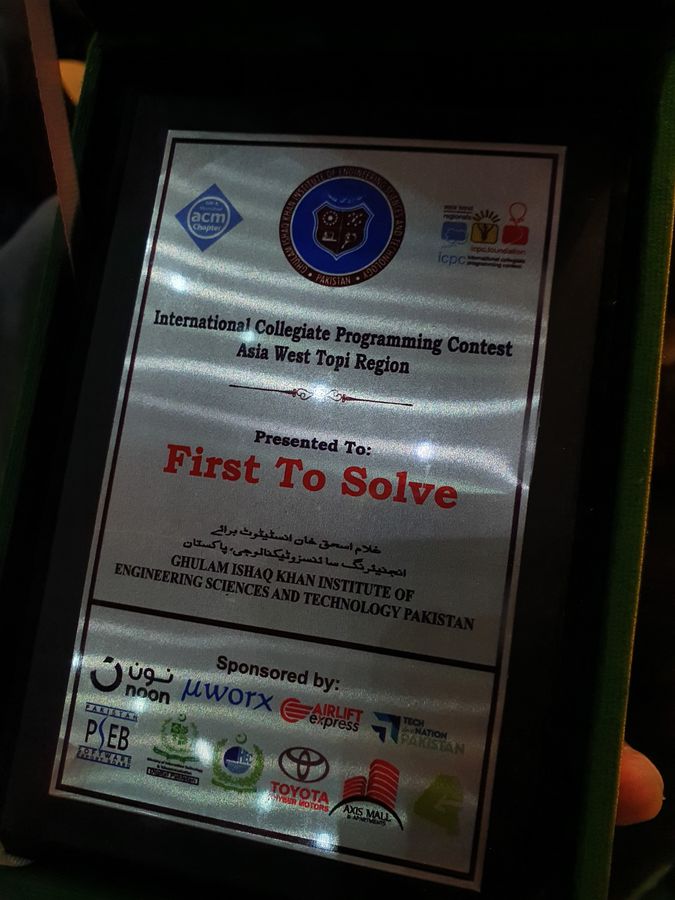
  • First To Solve award for a contest problem.

Pakistan Cyberhackathon

2021

National competition organized by the Government of Pakistan, 30 teams

  • 4th place in Capture the Flag, covering web, crypto, reversing, forensics, network, pwn and Linux privilege escalation.
  • 4th place in Web Application Exploitation.
  • 5th place in Speed Programming.

University competitions

2019 to 2021

  • Debug Your Soul, 2019: winners, team lead.
  • Bug Catcher, NASCON 2019: runners-up.
  • Think Tank, FAST NUCES 2021: winners, team lead.

education

FAST NUCES, Islamabad

2018 to 2022

BS Computer Science, specialization in Cyber Security, CGPA 3.59

Ethical Hacking

Multiplayer game hacking: memory editing, pointer scanning and code injection, and analysis of the game's anti-cheat. Desktop application pentesting: intercepting client-server traffic and patching binaries to bypass application logic.

Information Security

Visual cryptography: modified RSA for encrypting images, sent over Python sockets. Securing web applications and web services: fixed OWASP Top 10 issues, hardened auth and sessions, secured APIs, and configured TLS and security headers.

Malware Analysis

Static and dynamic analysis of real-world samples in a sandbox with Ghidra and IDA. Wrote a sample to understand the attacker side. Application reverse engineering.

Low-level background: an x86 assembly game in MASM and a multi-threaded C++ raytracer.

AWS Certified Cloud Practitioner, 2022 to 2025 (expired).

skills

Offensive
Web app testing, WAF and bot protection bypass, TLS/JA3 fingerprinting, anti-bot JS reversing, binary patching, game hacking
Reverse engineering
Ghidra, IDA, Frida, SSL pinning bypass, static and dynamic malware analysis
Defensive
Security audits, RBAC and least-privilege IAM, audit logging, Cloudflare WAF and bot management, business logic testing, fraud detection, OWASP Top 10, JWT and OAuth, security headers, Dependabot, anomaly alerting
Tools
Burp Suite, Wireshark
Cloud
AWS (EC2, ECS, EFS, S3), Docker, Kubernetes, Linux
Automation and AI
LLM-generated crawlers, agentic workflows, automated block detection and recovery
Languages
Python, TypeScript, JavaScript, C/C++, SQL, x86 assembly
Backend
FastAPI, Flask, Scrapy, Shopify apps, RabbitMQ, PostgreSQL, MongoDB

contact

Email ubaidullah0504@gmail.com, or find me on LinkedIn and GitHub.